 SimpleACME
A DNS plugin that can update an authoritative zone does not necessarily follow a CNAME to another zone before writing. That distinction explains why RFC 2136 setups can work for direct TXT owners yet fail after delegation. Decide whether to use a restricted dynamic-update policy on an authoritative server you operate or a client integration designed for an existing ACME-DNS account. Verify both the update destination and the CA-visible answer rather than mixing the two models accidentally.
This guide addresses a problem raised in a public r/letsencrypt discussion. The discussion identifies the question; the runbook below is our own explanation, not a claim that the original poster used or endorsed SimpleACME. Read the source discussion for its historical context and compare it with the current client documentation linked below.
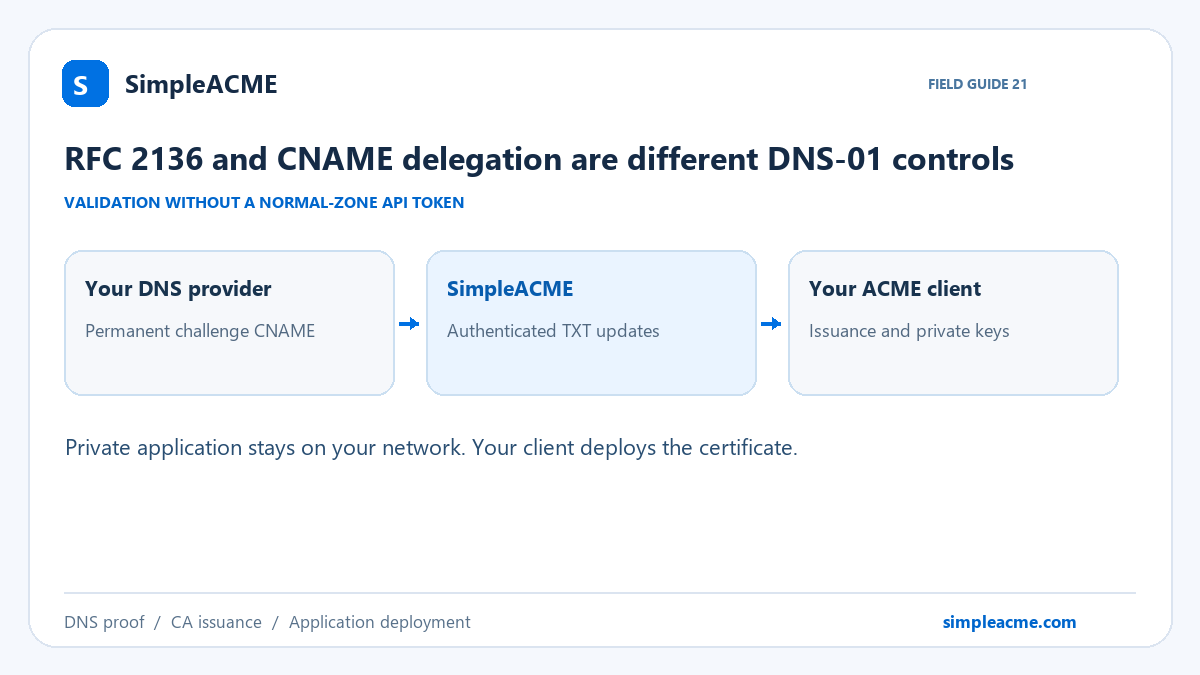
Reduce scope without hiding the remaining authority
The useful security question is what a stolen credential would let an attacker do. A normal-zone administrator token may permit changes far beyond certificate validation. A delegated challenge credential has a narrower purpose, but it still grants meaningful authority over validation for the names using that delegation. Protect it with the same care you give other operational secrets.
Keep secrets out of repositories, screenshots, process transcripts and web-accessible files. Restrict which hosts and task identities can read the mapping, and include protected backups in the access review. After exposure, rotate or replace the affected registration using the supported service process and update the CNAME deliberately when needed. Also consider the private keys held by the client. Reducing DNS credential scope does not repair a compromised application host or remove the need for incident response.
Start with these three checks
- Confirm which zone and owner the plugin actually sends in its update request.
- Use a narrowly scoped TSIG update policy if maintaining RFC 2136 yourself.
- For SimpleACME use the supported existing-account hook rather than an unrelated zone writer.
Work through the checks against the running system, not only the configuration you expected to deploy. Save a short record of the observed answer, the client version and the first failing log message. Make one relevant change at a time so you can tell whether it corrected the original failure. Keep real credentials and private-key contents out of that record.
Configure Certbot with a stable delegation
Prepare the intended name in your SimpleACME account and copy its exact challenge CNAME. A free account can prepare one single-domain demo, but DNS updates are blocked until paid access is active. Paid single-domain and wildcard registrations follow accepted payment. Choose the required coverage deliberately; a registration or a plan label is not proof that every certificate identifier is included.
Add the CNAME at your existing authoritative DNS provider. Preserve it for later renewals, and configure the client to update the existing registration it points to. You do not need to share the normal DNS provider's API credentials with the renewal host. Your existing website and email DNS stay where they are. A CNAME is needed per distinct challenge owner, rather than one record for an unrelated collection of hostnames.
Certbot's manual DNS mode becomes unattended only when the presentation work is handled by a suitable authentication hook. The hook receives the current validation value from Certbot, selects the existing account mapping and publishes the proof through SimpleACME. It must report update failures and wait for the answer to be visible before returning success. A shell command that merely prints instructions is still a manual process.
Keep the saved renewal lineage, hooks and mapping persistent. In Docker, bind-mount the complete certificate directory because the live paths can depend on archive files and saved renewal configuration. Configure a deployment hook for the actual consumer. A successful certonly operation does not automatically mean Nginx, Apache, a NAS or another application has loaded the new certificate. Use the active-subscriber guide for the reviewed Bash hook and Docker example, then adapt paths and permissions to your installation.
Test the result at all three boundaries
Begin with a staging validation using a separate test certificate configuration where the client supports it. Check the final public DNS answer before asking the CA to validate. These read-only examples use illustrative names; replace them with the exact challenge owner and hostname from your own setup:
dig +short CNAME _acme-challenge.app.example.com
dig +short TXT _acme-challenge.app.example.com
openssl s_client -connect app.example.com:443 -servername app.example.com </dev/null
Then inspect the client result to confirm that the CA actually issued a certificate. Finally, inspect the certificate served by the target application from the relevant user network. Compare its names and expiration with the issued object. Test the unattended job again after a controlled restart or container recreation. Record how you would recover if the validation host or deployment target became unavailable.
Know the service boundary before relying on it
SimpleACME uses its authenticated update API. It does not turn into a general RFC 2136 authoritative-zone update endpoint.
SimpleACME records TXT authorization changes and can send optional DNS-change notifications. That timeline is useful evidence, but it cannot confirm issuance or installation performed by your independent client. Keep a separate served-certificate expiry check and review update entitlement before the paid-through date. Yearly subscription billing is not the certificate validity period; let the ACME client renew when its authority and renewal policy require it.
Frequently asked questions
Does SimpleACME fix this entire problem automatically?
SimpleACME uses its authenticated update API. It does not turn into a general RFC 2136 authoritative-zone update endpoint. The delegated workflow removes the normal-zone API dependency from DNS presentation. The diagnosis, client configuration and application verification described above still matter. Use the three concrete checks in this guide to identify which part of the system needs repair before changing unrelated infrastructure.
What should stay unchanged after the first successful setup?
Keep the assigned challenge CNAME, the existing registration mapping and the supported client workflow persistent. The authorization TXT value changes for new validations; the delegation normally does not. If you replace a registration, migrate the corresponding mapping and DNS record together. Recheck the public answer and complete an unattended staging test before depending on the replacement.
How do I know renewal is complete?
Treat a successful TXT update, successful CA issuance and correct application deployment as separate results. Inspect client logs, validate the issued certificate and probe the endpoint using the correct hostname. A browser showing an old certificate is a reason to inspect routing, bindings and reload behavior, even when DNS presentation worked. Maintain an independent expiry alert for the service users actually reach.
References and the next step
Use the SimpleACME Certbot guide for supported setup details and the subscriber how-to library for the reviewed configuration and script examples. Consult the primary references below for the installed client's current options. If this matches your constraints, create an account and prepare your domain, verify the CNAME, then activate the required update access before a production validation.